0191 543 3432 info@cyberfits.co.uk Monday to Friday, 8:00am to 5:00pm
Free IT review
Security awareness training

Help your team spot scams and feel confident reporting them

Technology stops most threats, but some always reach a person. Short, regular training and realistic phishing tests help your staff recognise scams, and a no blame reporting culture means problems are dealt with quickly.

At a glance

  • Short online training modules
  • Realistic simulated phishing emails
  • Simple, practical security policies
  • A no blame culture of reporting

Bite sized training

Short online lessons on phishing, passwords, safe browsing and handling data, designed to fit around a busy working day.

Simulated phishing

Safe test emails that look like real scams. Anyone who clicks sees a short explanation of what they missed, not a telling off.

Progress reporting

Reports show who has completed training and how the team responds to tests, so you can see improvement over time.

Clear policies

Plain English policies covering passwords, devices, email, remote working and what to do if something goes wrong.

Easy reporting

A simple way for staff to report suspicious emails and a promise that we will look at them quickly and without judgement.

New starter induction

Security basics included when new people join, so good habits start on day one.

Security awareness training

Why people matter as much as technology

Email filters, endpoint protection and multi factor authentication stop most attacks. But criminals know this, so they increasingly target people directly: a convincing email from the boss asking for an urgent payment, a phone call claiming to be from IT, or a fake login page that looks exactly like Microsoft.

Training is not about making staff feel foolish or scared. It is about giving them the confidence to pause, check and ask when something feels wrong, and making sure they know exactly who to tell.

We provide training as part of our cyber security services, alongside the technical protections that catch most threats before people ever see them.

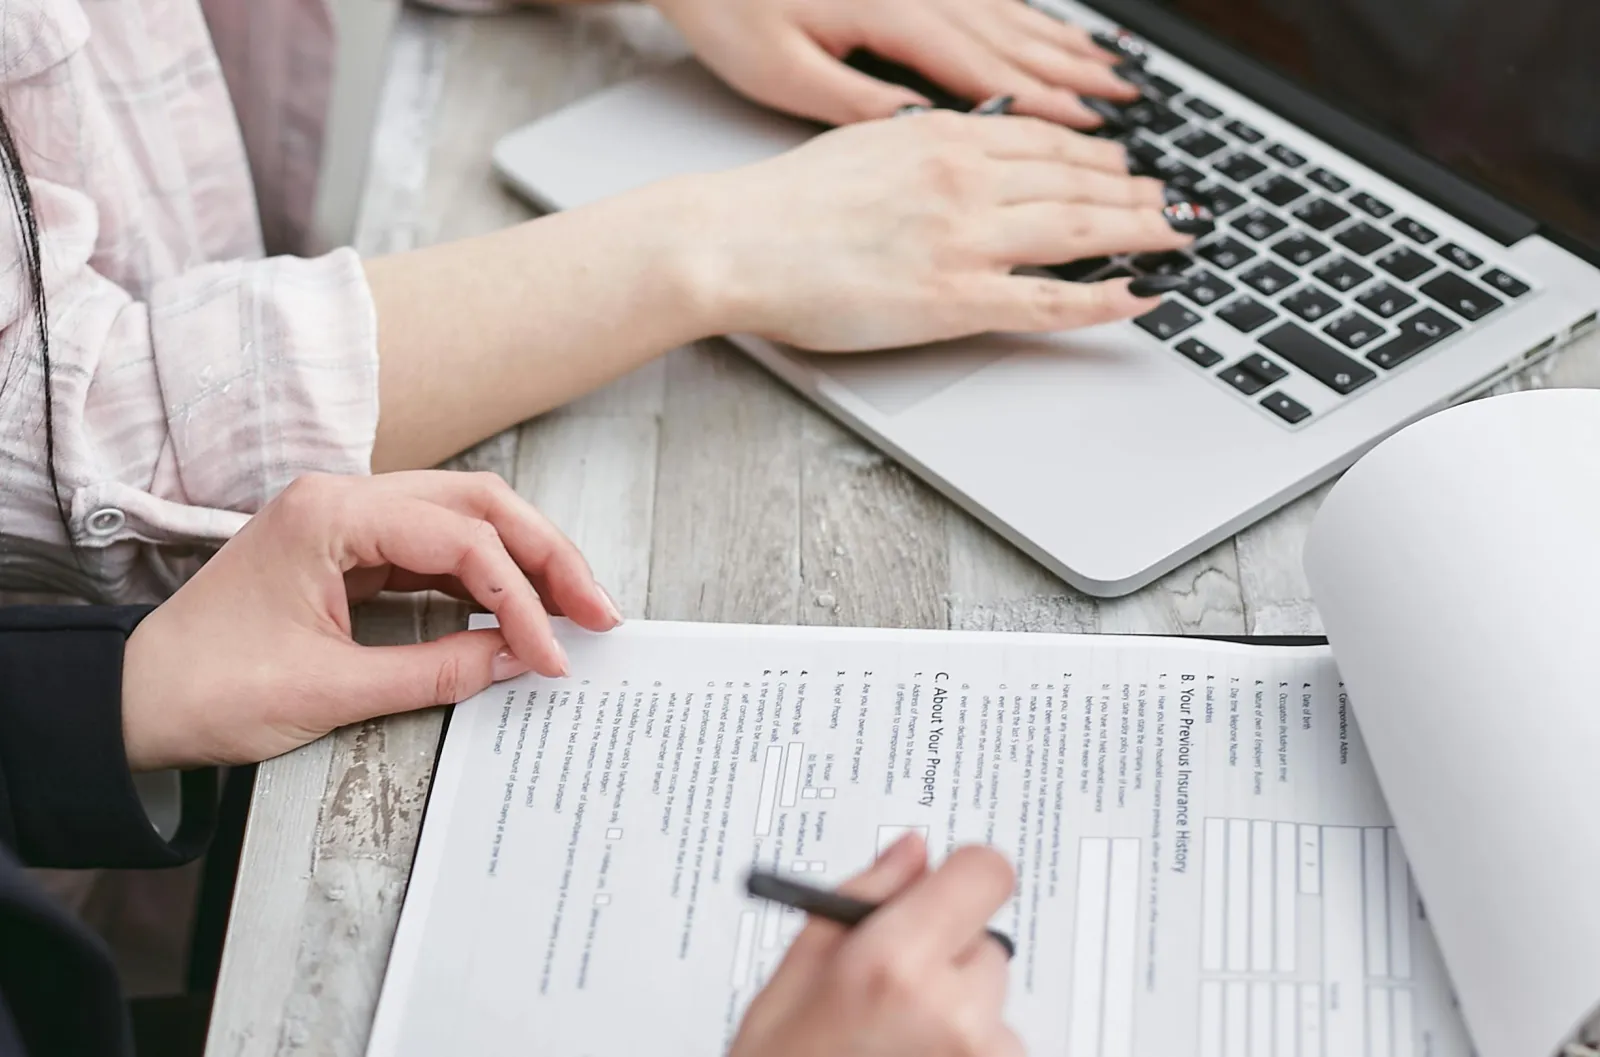
Colleagues working through training on their laptops
What you get

What a training programme can include

  • Online security awareness courses
  • Regular simulated phishing campaigns
  • Completion and progress reports
  • Acceptable use and password policies
  • Remote and hybrid working guidance
  • Payment and bank detail change procedures
  • Incident reporting process
  • Security induction for new starters
  • Refresher training through the year
  • Briefings for managers and directors

Training is most effective alongside email security and endpoint protection, so fewer threats reach your team in the first place.

How it works

From first conversation to fully looked after

Baseline

We agree the approach with you and can run an initial simulated phishing test to see where your team is starting from.

Train

Staff complete short online modules at a pace that suits your business, covering the threats they are most likely to see.

Test and reinforce

Regular simulated phishing emails keep awareness fresh, with instant feedback for anyone who clicks.

Review

We share progress reports with you and adjust the training to focus on the areas that need it most.

What is security awareness training?

Security awareness training teaches staff to recognise and respond to the cyber threats they are most likely to meet at work. For most small businesses, that means phishing emails, fake invoices, password theft, scam phone calls and mistakes with personal data.

Good training is short, regular and practical. A single long session once a year is quickly forgotten. A few minutes every month, combined with realistic tests, builds habits that last. We use VIPRE Security Awareness Training, which provides short online modules and simulated phishing campaigns that we set up and manage for you.

What your team will learn

  • Spotting phishing. Checking the real sender address, hovering over links, being wary of urgency and unexpected attachments, and recognising fake login pages.
  • Passwords and sign ins. Using long, unique passwords or a password manager, why multi factor authentication matters and never approving a sign in prompt you did not expect.
  • Payment fraud. Always verifying requests to change bank details or make urgent payments by phoning a known number.
  • Handling data. Sending personal information safely, checking recipients and what counts as a data breach under UK GDPR.
  • Working safely anywhere. Locking screens, using public WiFi carefully and keeping work data on work systems.
  • What to do if something goes wrong. Who to tell, how quickly and why it matters.

How simulated phishing works

A simulated phishing campaign sends safe test emails to your staff that look like the scams they might receive: a missed delivery notice, a shared document or a password expiry warning. Nothing harmful happens if someone clicks. Instead, they see a short page explaining the clues they missed.

Over time, the reports show how many people click, how many report the email and how that changes. The aim is not to catch people out. It is to give everyone practice in a safe setting so they are ready for the real thing. We keep tests realistic but fair, and we agree the approach with you beforehand.

Building a reporting culture

The most important outcome of training is not that nobody ever clicks a bad link. It is that when someone does, they tell someone straight away. A password reset within minutes of a mistake can prevent a serious incident; the same mistake hidden for a week can be very costly.

That only happens if staff trust that reporting will not get them into trouble. We encourage a no blame approach, give staff a simple way to report suspicious emails and respond quickly to every report. Thanking people for reporting, even when the email turns out to be harmless, is one of the most effective things a manager can do.

Policies that people can actually follow

Policies help set expectations, but only if they are short and clear. We can help you put together plain English policies on acceptable use, passwords and multi factor authentication, using personal devices for work, remote working, handling personal data and reporting incidents. They also help if you are working towards Cyber Essentials, responding to a client security questionnaire or completing a cyber insurance application.

Training for directors and managers

Directors and finance staff are often targeted specifically, because they can approve payments and have access to sensitive information. We can provide short briefings for leadership teams covering the threats aimed at them, the decisions that need to be made in an incident and the questions to ask about your security. The UK National Cyber Security Centre also publishes free guidance for small businesses that we can point you towards.

Keeping it going

The benefit of training fades if it stops. We recommend short refresher modules through the year, regular simulated phishing tests that change over time and adding security to the induction for every new starter. We review the reports with you and focus future training on the areas where your team needs the most help.

Part of a wider security approach

Training works best alongside technical protections. Email security reduces how many scams reach inboxes. Endpoint protection catches malware if someone does open a bad attachment. Multi factor authentication protects accounts if a password is entered on a fake page. Together, these layers mean one mistake is far less likely to become a serious problem.

If you would like to make your team a stronger line of defence, get in touch or call us on 0191 543 3432.
Questions

Security awareness training: your questions answered

How long does the training take?

Most modules take just a few minutes, so staff can complete them between other tasks. Short, regular training is more effective than one long annual session.

Will staff be told off if they click a simulated phishing email?

No. Anyone who clicks sees a short explanation of the clues they missed. The aim is to learn in a safe setting, and we encourage a no blame approach so people feel comfortable reporting real mistakes.

Do we need to tell staff about phishing tests in advance?

We usually recommend telling staff that simulated phishing tests will happen as part of training, without saying when. That keeps the tests realistic while being open and fair with your team.

Can you write our security policies?

Yes. We can help you put together short, plain English policies covering acceptable use, passwords, devices, remote working, data handling and incident reporting, tailored to how your business works.

Does training help with cyber insurance?

Many cyber insurance applications ask whether staff receive security training. Having a training programme and reports showing completion can help you answer those questions accurately. Check your own policy for its specific requirements.

Is training included in managed IT support?

It depends on the plan you choose. Training can be included or added as a separate service. We will explain the options when we discuss your requirements.

Let's talk

Ready for IT that just works?

Book a free, no obligation IT review. We will look at your setup, tell you honestly what needs attention and give you a clear fixed monthly price.

Call us Free IT review